Stale Intelligence
Yesterday's Safe Can Be Today's Threat
Attackers constantly rotate IPs, domains, and infrastructure. Static intelligence creates blind spots when threats change faster than your defenses.
Social Engineering is on the rise
Curated, validated threat intelligence delivered directly into your security stack, the moment a new threat is confirmed.
Threat actors move fast. Your security tools need intelligence that moves faster.
Stale Intelligence
Attackers constantly rotate IPs, domains, and infrastructure. Static intelligence creates blind spots when threats change faster than your defenses.
Manual Integration
Collecting intelligence, formatting indicators, and manually feeding security tools consumes valuable analyst time.
Unvalidated Feeds
Unvalidated open-source feeds flood your team with low-quality indicators, creating noise and making real threats harder to spot.
Digital brand abuse appears across multiple channels simultaneously. TechOwl Shield delivers unified monitoring and enforcement across domains, social media, applications, repositories, and online marketplaces through a single intelligence driven protection layer.
Confirmed malicious IPs linked to C2 servers, scanners, botnets, and attacker infrastructure.
Verified domains associated with phishing, C2 activity, malware distribution, and suspicious infrastructure.
Confirmed malicious URLs used in phishing, malware delivery, and credential harvesting campaigns.
Known malware samples identified through SHA256, MD5, and SHA1 hashes.
ThreatPulse delivers curated, high-fidelity Indicators of Compromise directly into your security ecosystem through TAXII 2.1. Every indicator is validated, filtered, and enriched before it reaches your tools.
See More of the Threat Landscape
Continuously aggregate intelligence from global threat sources across malicious IPs, domains, URLs, and file hashes.
Trust the Signal
Validate every indicator and filter false positives before publication, so your team focuses on threats that matter.
Put Intelligence to Work
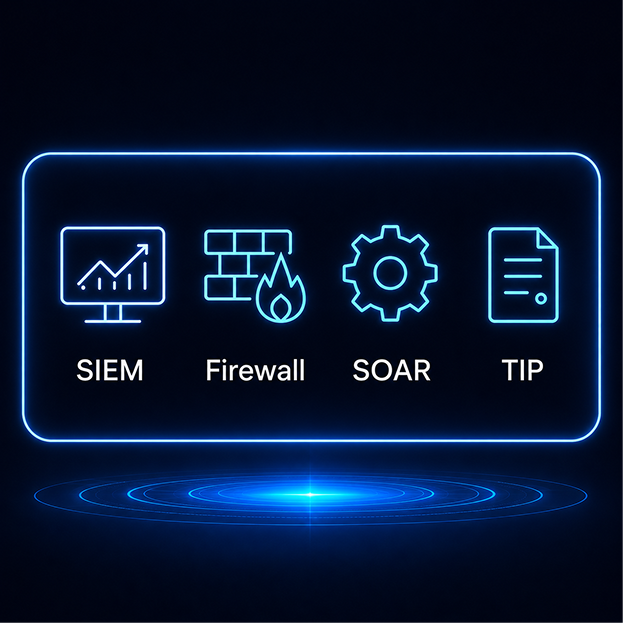
Automatically deliver confirmed IOCs to your SIEM, firewall, SOAR, TIP, and other security tools through TAXII 2.1.
Industry-standard threat intelligence delivery designed for seamless integration.
Machine-readable threat context including type, category, and first-seen and last-seen information.
Keep your defenses aligned with the latest confirmed indicators without manual refresh cycles.
Authenticated and encrypted connections keep intelligence protected in transit.
Enrich detections and alert context
Trigger automated response playbooks
Block malicious infrastructure at the perimeter
Combine ThreatPulse with your broader intelligence ecosystem
Push confirmed malicious indicators into security controls before they reach your environment.
Automate collection, validation, and delivery so analysts spend less time managing feeds.
Add confirmed threat context to detections instead of investigating raw indicators.
Filter out low-quality and legitimate infrastructure before indicators reach your tools.
Reduce investigation time with contextual intelligence available when your team needs it.
Keep your security controls aligned with an evolving threat landscape.
ThreatPulse is built to prioritize intelligence your security team can trust.
No unvetted community submissions. Every indicator is reviewed and validated before publication.
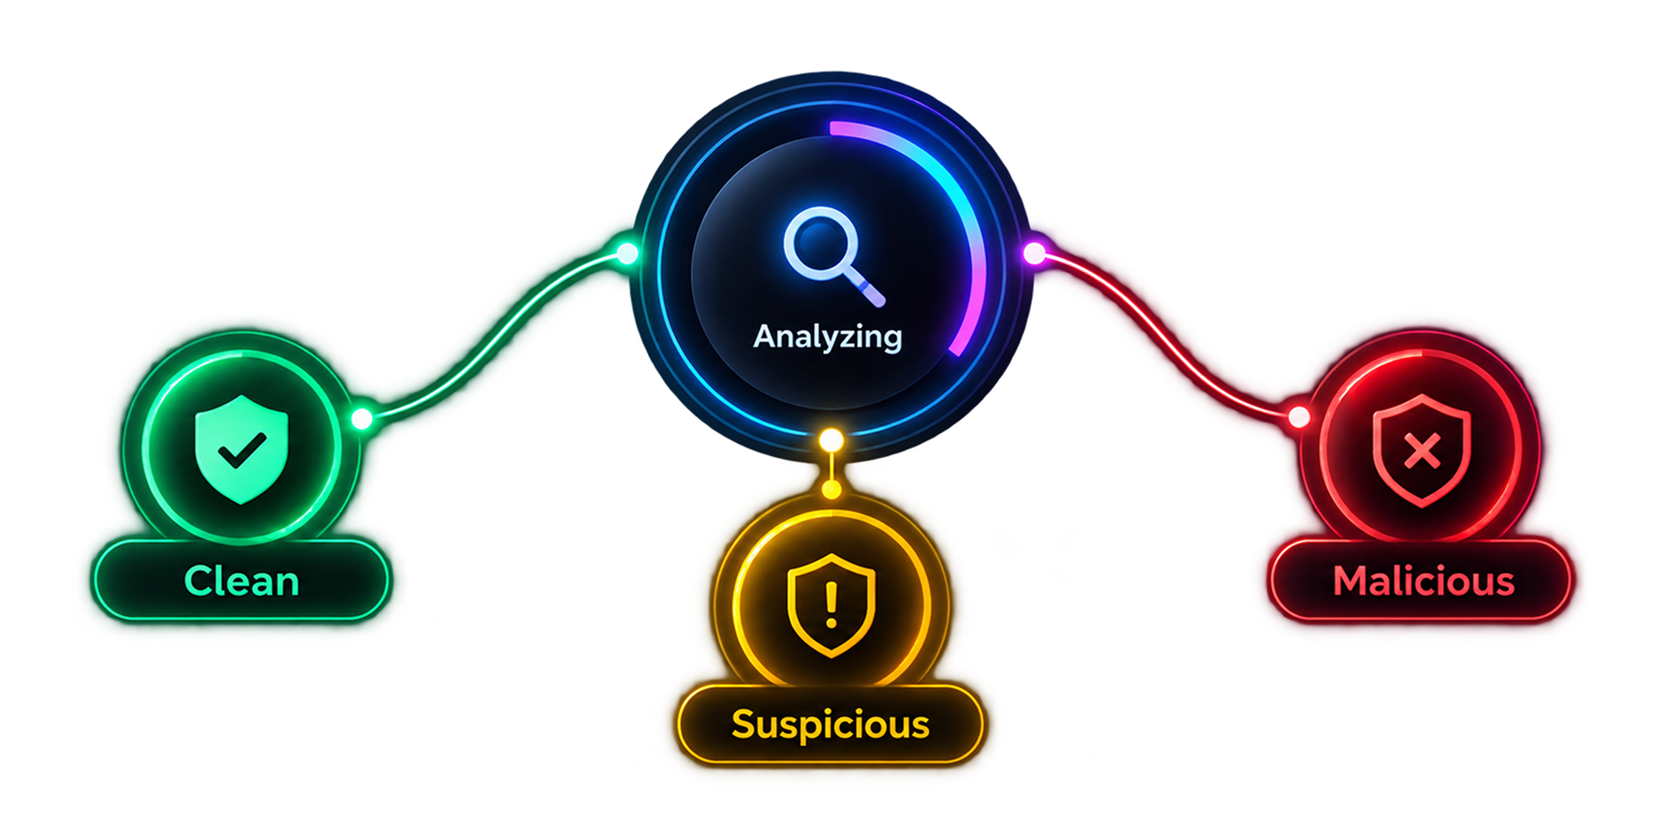
Investigate any IP, domain, URL, or file hash against the ThreatPulse intelligence database.
Legitimate infrastructure, CDNs, and known-safe services are filtered before indicators reach your environment.
Check suspicious IPs against C2, botnet, scanner, and malicious infrastructure intelligence.
Identify phishing, C2, malware distribution, and suspicious newly registered domains.
Determine whether a URL has been associated with active phishing or malware delivery campaigns.
Check SHA256, MD5, and SHA1 hashes against known malware intelligence.
Threat intelligence is more than a feed. It is evidence that your defenses are continuously informed by the threat landscape.
Demonstrate that threat intelligence is actively informing detection controls.
Provide documented intelligence sources and monitoring practices for review.
Strengthen your ability to identify and respond to known threats.
Support Detect and Respond functions with intelligence-led security controls.
Threat Signal Intelligence
Attack Surface Monitoring
.png)
Email Trust Assurance
.png)
Advanced Threat Detonation
.png)
Employee Risk Readiness
.png)
Cloud Security Visibility
.png)
Third-Party Risk Intelligence
.png)
Breach & Attack Simulation
Connect ThreatPulse to your security stack in minutes.