EC2 · S3 · RDS · IAM · Lambda · VPC · CloudTrail · 100+ Services
Continuous cloud security posture management that finds misconfigurations, reduces risk, and keeps your cloud secure and compliant before attackers find the gaps.
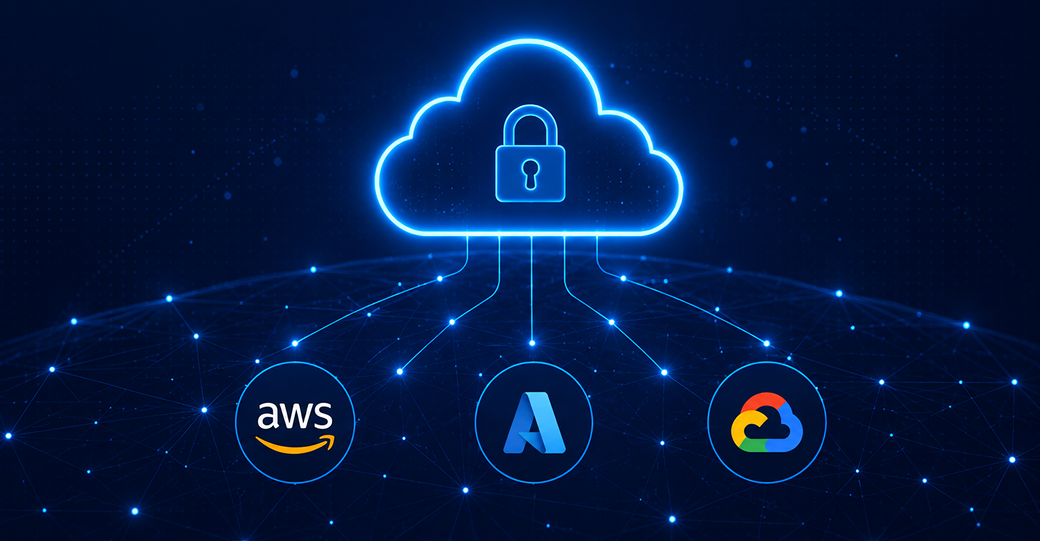
Book a DemoBring your entire cloud security posture into one unified view, no matter where your workloads live.
EC2 · S3 · RDS · IAM · Lambda · VPC · CloudTrail · 100+ Services
Virtual Machines · Blob Storage · Azure AD · NSGs · Key Vault · Azure Services
GCE · GCS · BigQuery · Cloud IAM · VPC Firewall · GCP Services
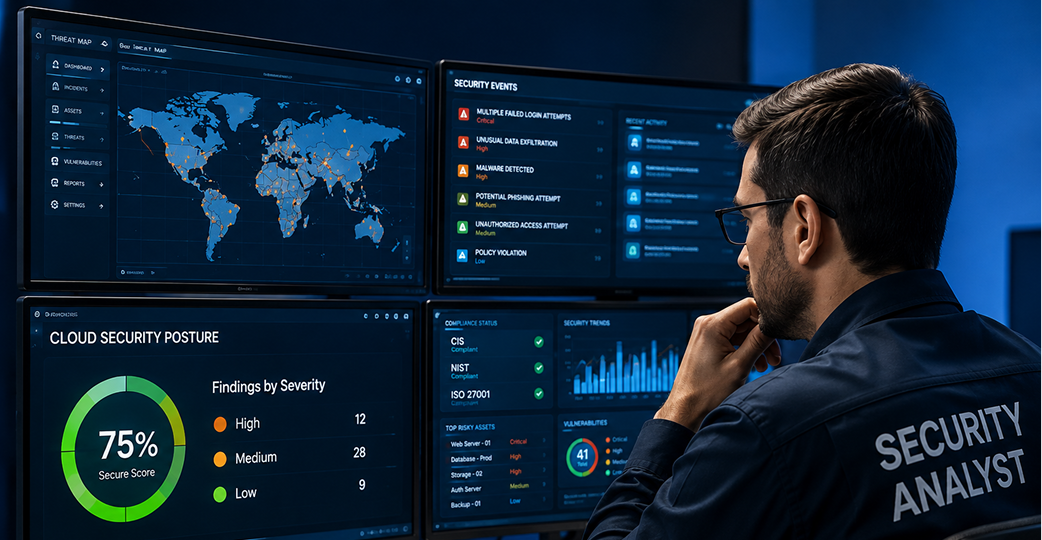
TechOwl CSPM gives security teams one unified view of their cloud posture across accounts, regions, providers, and services, helping them discover risk, enforce policy, and prove compliance continuously.
3
Major Cloud Providers Covered
82%
Cloud Breaches Involve Misconfigurations
100%
Continuous Posture Visibility
From asset discovery to compliance reporting, TechOwl CSPM gives your security team the visibility and control to stay ahead of cloud risk.
See every cloud asset, account, region, service, and identity from one continuously updated security view.
Catch exposed storage, open ports, excessive permissions, and insecure configurations as soon as they appear.
Identify over-privileged accounts, unused credentials, and excessive permissions that can enable lateral movement.
Continuously map your cloud posture against industry frameworks and internal policies.
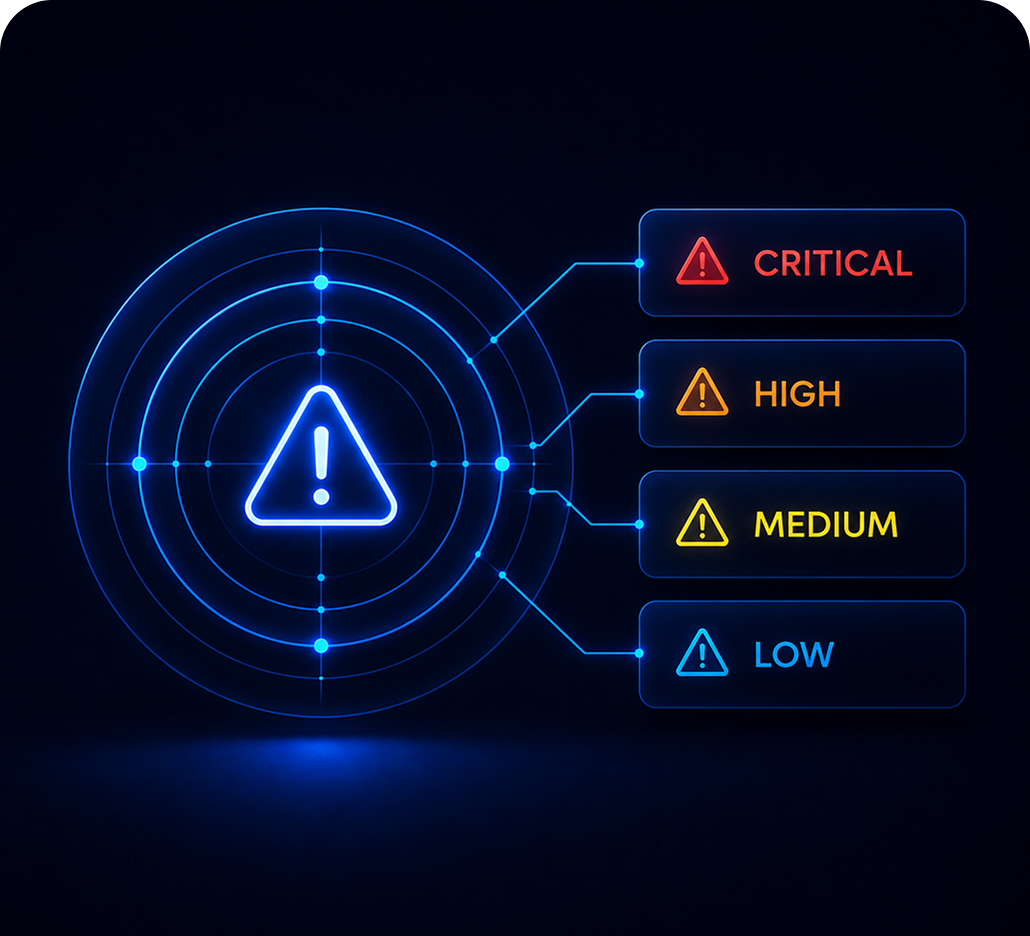
Know exactly what needs attention first, with risk-based prioritization and step-by-step remediation guidance.
Track risk trends, compliance scores, and security improvements through clear, board-ready dashboards and reports.
Periodic audits cannot keep pace with dynamic cloud environments. TechOwl CSPM continuously monitors your cloud, detects posture drift, and helps your teams act before small gaps become major exposures.
Monitor AWS, Azure, and GCP from one unified security posture.
Detect security gaps in real time instead of waiting for the next quarterly audit.
Prioritize the issues that create the greatest real-world exposure.
Automatically inventory your cloud environment across providers, accounts, regions, services, and identities.
Continuously evaluate your cloud posture against security frameworks, compliance requirements, and internal policies.
Detect policy drift, apply security guardrails, and guide teams through remediation before risk becomes a breach.
Generate compliance evidence, security reports, and posture insights that demonstrate continuous control.
Include a comprehensive project overview, specifying the genre, providing a synopsis, detailing your team. Attach supporting materials, whether it's a script and portfolio.
Monitor VMs, containers, and serverless workloads for insecure configurations and exposed services.
Identify public access, encryption gaps, and risky configurations across buckets, databases, and file stores.
Validate security groups, firewall rules, and network configurations against least-privilege principles.
Detect excessive permissions, over-privileged roles, inactive credentials, and risky access paths.
Continuously assess your entire cloud environment against active frameworks and internal security policies.
Real-time detection reduces the window between exposure and remediation.
Identify excessive permissions and over-privileged access before they become attack paths.
Maintain a complete, always-current view of your cloud environment.
Risk-based prioritization helps teams focus on high-impact issues instead of security noise.
Keep compliance posture and control evidence continuously up to date.
Secure growing cloud environments without adding complexity or creating new blind spots.
Continuous compliance monitoring helps you maintain security standards every day, not just when an audit is approaching.
Track cloud posture against the security and compliance frameworks that matter to your business.
Identify failed controls and security gaps without manual assessments.
Generate reports and evidence that demonstrate active security controls and continuous oversight.
Track security violations, posture changes, and remediation history over time.
Support cloud security requirements across highly regulated industries.
Give leadership a clear view of cloud security posture, compliance status, and risk trends.
Cloud Security
Visibility
.png)
Third-Party Risk Intelligence
Attack Surface Monitoring
.png)
Advanced Threat Detonation
.png)
Threat Signal Intelligence
.png)
Continuous Breach &
Attack Simulation
.png)
Email Trust Assurance
.png)
Employee Risk Readiness
Stop discovering cloud risk after the fact. Get continuous visibility, proactive risk detection, policy control, and compliance confidence across your entire cloud environment.