Submit
Upload suspicious files through the web portal or send them directly from your existing security tools using the API.
Cloud-Native Malware Analysis
Detonate, analyze, and understand suspicious files in minutes. ThreatLab gives your security team fast, actionable malware verdicts without the infrastructure, complexity, or waiting.
Manual investigation can consume hours for a single suspicious file. ThreatLab delivers a complete threat verdict in minutes.
Modern malware is built to evade signatures and traditional scanners. ThreatLab analyzes behavior, memory, network activity, and more to uncover what others miss.
Building and maintaining your own malware analysis environment requires time, expertise, and constant upkeep. ThreatLab gives you cloud-native analysis without the infrastructure burden.
Submit a file. Let ThreatLab detonate it in a secure environment. Get the intelligence your team needs to act.
Upload suspicious files through the web portal or send them directly from your existing security tools using the API.
STEP
01
STEP
02
ThreatLab safely detonates the file in an isolated cloud environment and monitors every action, connection, and behavior.
Receive a clear verdict with risk scoring, IOCs, attack timelines, and MITRE ATT&CK mapping so your team can respond immediately.
STEP
03
ThreatLab goes beyond signatures to uncover the behaviors, connections, and techniques that reveal what a suspicious file is really doing.
From ransomware to zero-days, ThreatLab analyzes modern threats across Windows and Linux environments to help your team understand what happened before the damage spreads.
Detect in-memory attacks and script-based threats designed to leave little or no trace on disk.
Identify unknown threats through behavior and execution patterns beyond traditional signatures.
Expose stealthy attacker behavior and long-term persistence through behavioral analysis.
Uncover hidden remote access, persistence mechanisms, and malicious payloads.
Detect encryption activity, ransom behavior, & attempts to disable recovery mechanisms.
Identify PowerShell abuse, malicious macros, and living-off-the-land techniques.
Every analysis generates a structured report that turns complex malware behavior into clear, actionable intelligence for analysts, incident responders, and leadership.
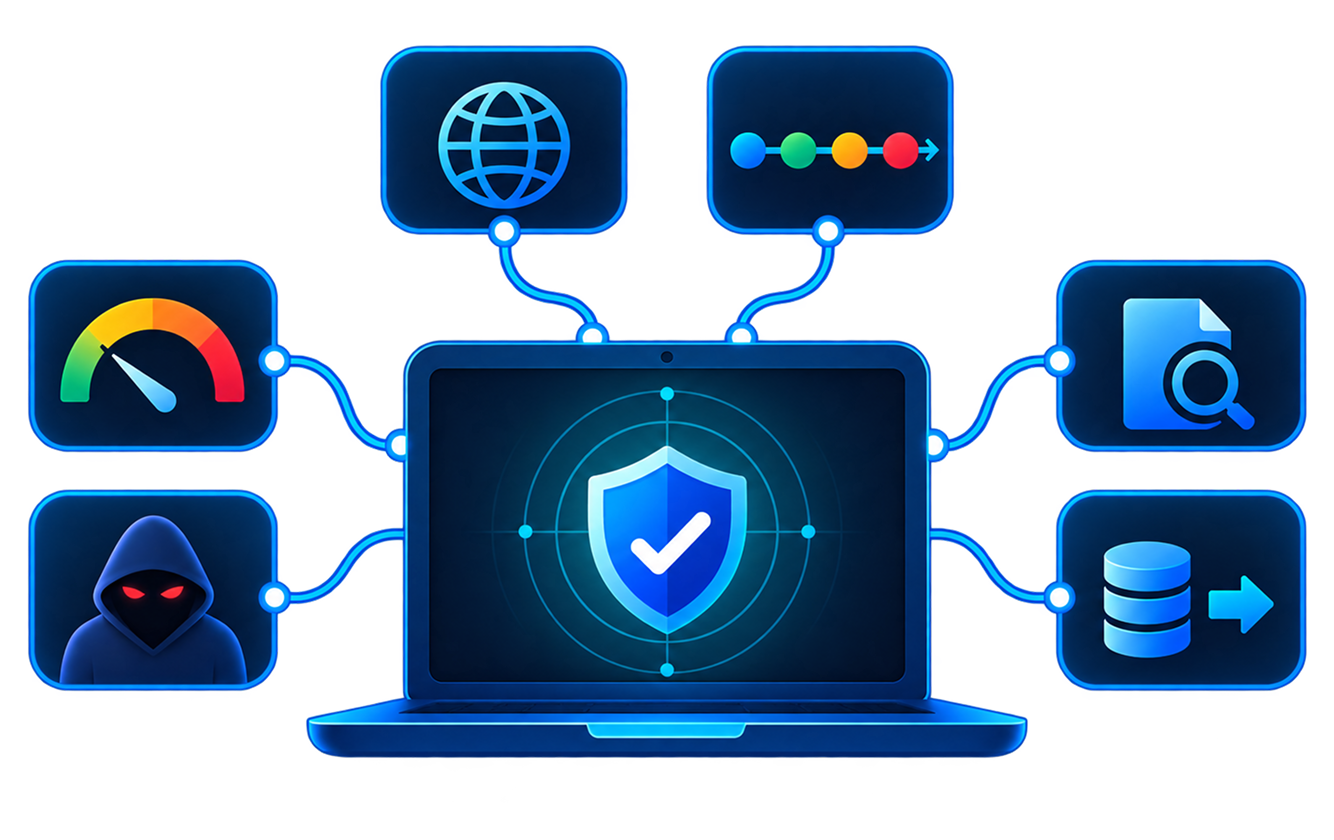
Safe, Suspicious, or Malicious with a 0 to 100 risk score.
Extract IPs, domains, hashes, and behavioral indicators ready for investigation or blocking.
See exactly what happened from execution to final activity.
Understand the techniques and tactics behind the attack.
Give leadership a clear understanding of the threat without overwhelming technical detail.
Send structured findings directly into existing security operations workflows.
Your submitted files, reports, and findings remain within TechOwl's secure infrastructure and are never shared or sold to third parties.
Data is protected in transit and at rest with enterprise-grade security controls.
Your organization's submissions and analysis results remain logically separated from other customers.
No hardware to deploy. No analysis infrastructure to patch. No environment to maintain.

Move beyond manual file triage. Get fast verdicts and keep your SOC queue moving.

Automatically analyze suspicious files and alerts as they surface from endpoint environments.

Proactively investigate suspicious files, samples, and indicators before they become incidents.

Understand what a threat executed, where it connected, and what it attempted to access.
Advanced Threat
Detonation
.png)
Third-Party Risk Intelligence
Attack Surface Monitoring
.png)
Threat Signal Intelligence
.png)
Cloud Security Visibility
.png)
Continuous Breach &
Attack Simulation
.png)
Email Trust Assurance
.png)
Employee Risk Readiness
Stop waiting for answers. Analyze suspicious files, uncover hidden behavior, and give your security team the intelligence to act faster.