Security Pulse
Real-Time Visibility Into Emerging Threat Activity
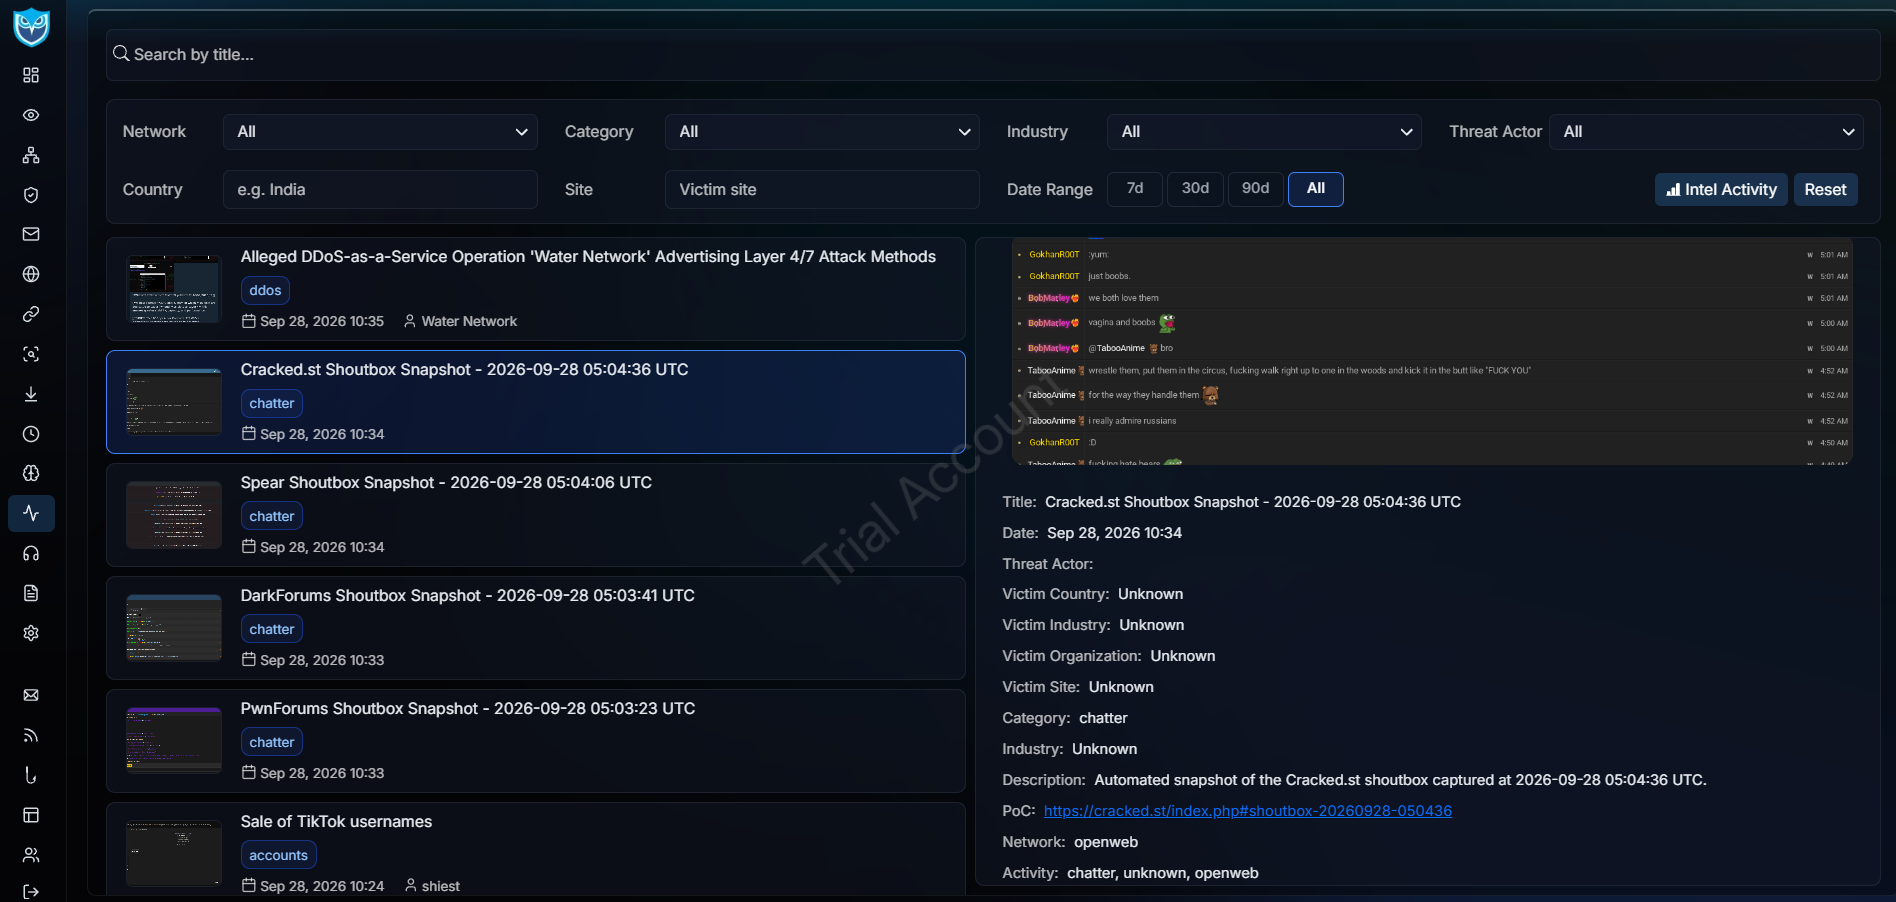
Security Pulse provides a live view of cyber activity observed across the threat landscape,
enabling teams to quickly understand what is happening, who is involved, who may be
targeted and how the attack is being carried out.
Security Pulse surfaces:
- Threat Actors associated with observed activity
- Actively Emerging Threats including DDoS, credential theft, carding
and underground activity
- Target Intelligence including affected countries, industries and
organizations
- Attack Details including activity type, infrastructure and observed
methods
- Source Intelligence with references and supporting evidence
Real-time threat activity → Context → Investigation
Threat Intelligence
Investigate Vulnerabilities With Actionable Technical Intelligence
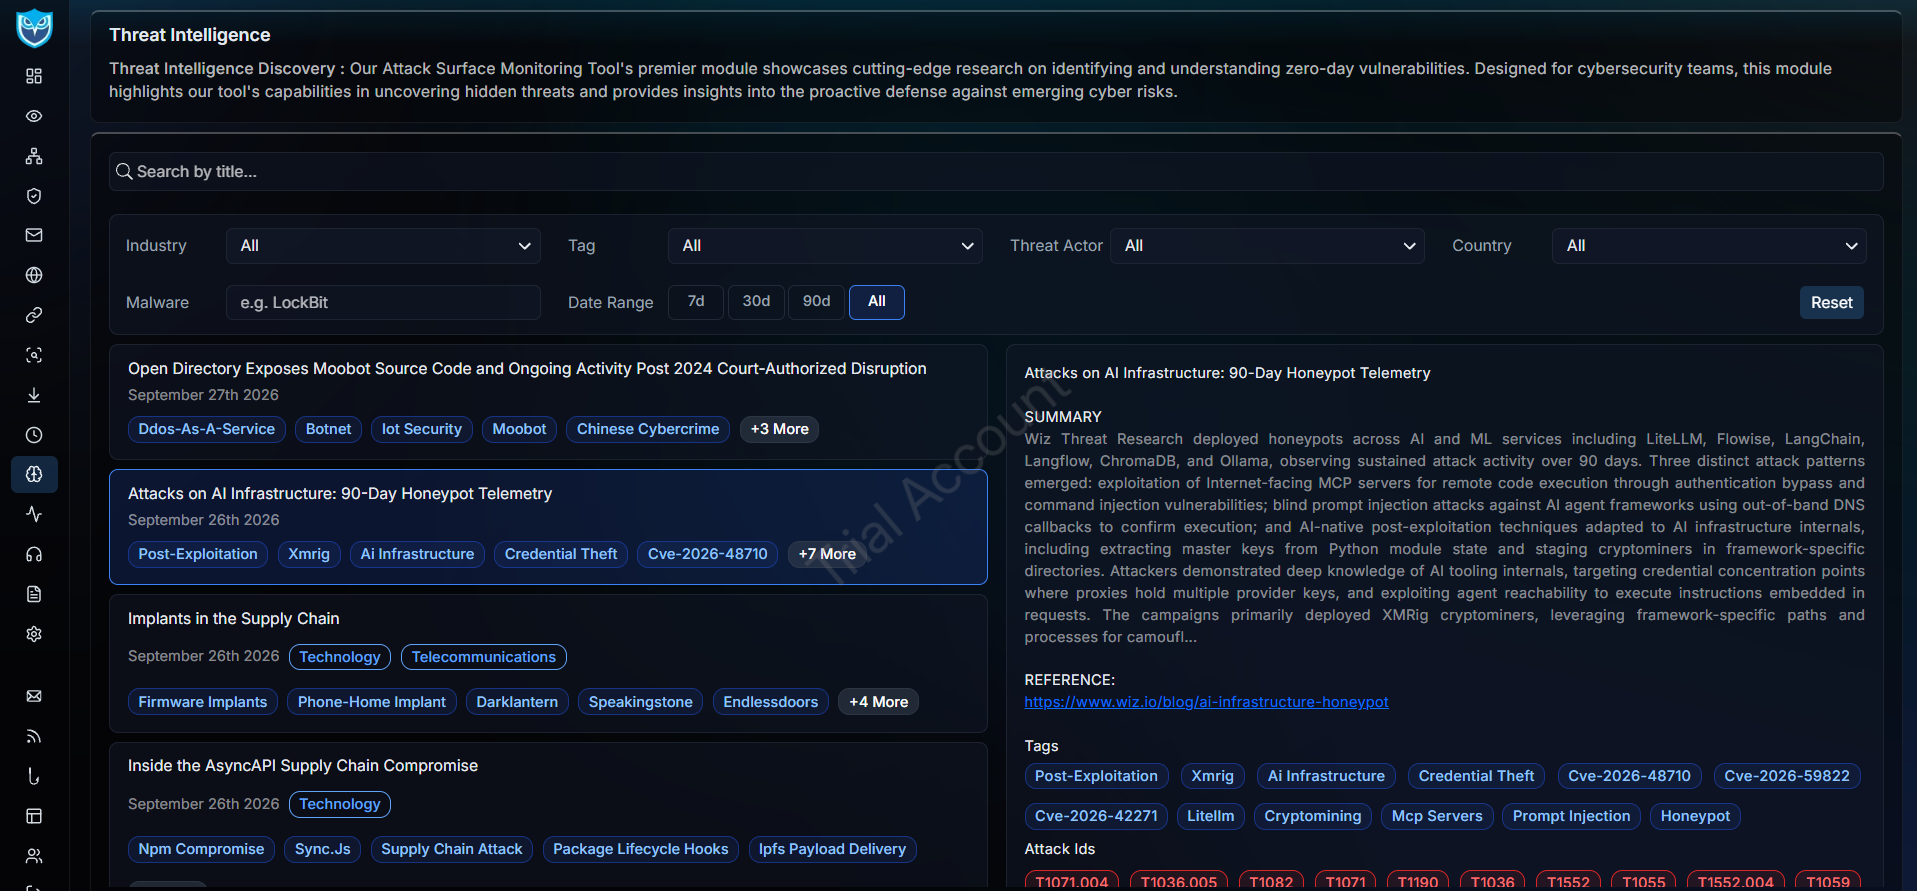
The Threat Intelligence module provides deeper research and technical context around
zero-day vulnerabilities, active attack campaigns, malware and supply-chain compromises.
Each intelligence record can provide:
- Vulnerabilities & Exploitation — emerging vulnerabilities
and associated attack activity
- IOCs — file hashes and other technical indicators linked to the
threat
- TTPs — mapped MITRE ATT&CK techniques and attack methods
- Threat Actors — actors, campaigns and associated activity
- Targeting — affected countries and industries
- Technical Context — malware, infrastructure, attack chain and
supporting research
- References — external sources supporting the intelligence
From Threat Detection to Threat Context
One platform. The intelligence needed to understand and investigate emerging threats.
| Capability |
What it gives you |
| Threat Activity |
Real-time visibility into emerging cyber
activity |
| Vulnerability Intelligence |
Intelligence on emerging and zero-day
vulnerabilities |
| IOCs & TTPs |
Technical indicators and MITRE ATT&CK
techniques |
| Threat Actor Context |
Actor, campaign and targeting information |
Why this matters
Turn real-time threat signals into actionable security intelligence.
- Discover — identify emerging threats and actively exploited
vulnerabilities.
- Understand — connect vulnerabilities with IOCs, TTPs, threat
actors and attack infrastructure.
- Investigate — access technical details, targeting information
and supporting intelligence.
- Respond — use contextual threat intelligence to support security
investigation and response.
